01
Agent visibility
Bring agent identities, owners, tools and observed behaviour into a shared inventory. Discovery coverage depends on the connected surfaces.
 UAE · AI integration
AI agent security & governance
On-premise security and governance for your AI agents. Keep the control plane, policy decisions and evidence inside your network, with an offline configuration using local models and internal systems.
CONTROL IN THE EXECUTION PATH
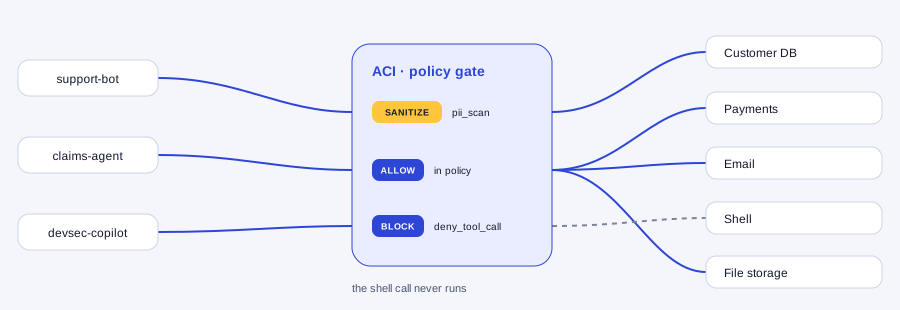
Discover the agent, evaluate the request, enforce the verdict and retain the evidence. Supported calls can be allowed, sanitised or blocked before they reach the next system.
01
Bring agent identities, owners, tools and observed behaviour into a shared inventory. Discovery coverage depends on the connected surfaces.
02
Evaluate governed prompts, responses and actions before dispatch. Allow, mask or block according to configured policies and supported integration coverage.
03
Run local sensitive-data checks before provider calls. Judge-based checks receive sanitised content; sanitised previews and audit metadata may still reach the configured control plane.
04
Apply rules to supported tools, shell operations, database queries and MCP invocations. Coverage and add-ons must be verified for each integration.
05
Inspect changes in agent behaviour, policy alignment and model use, with cost visibility and configured limits.
06
Review verdicts, matched policies and activity records. Evidence mapping supports reviews; it does not by itself establish certification or regulatory compliance.
DEPLOYMENT THAT FITS YOUR STACK
EgisAI documents in-process SDK governance, an inline gateway, self-hosted egress nodes and managed-browser discovery. Integration coverage, enforcement modes and package availability differ; we establish the right combination for your environment.
Tell us which agents you run, what they can access and where you need stronger control. We will work through the integration and governance requirements with your team.
Talk to us about ACI SovereignAdapted from EgisAI product and self-hosting materials reviewed 23 October 2026. Offline semantic checks require a local model endpoint. External SaaS connectors and public model APIs require connectivity. Features vary by integration and package; no supplier certification is claimed for appana.
ON-PREMISE / ENTERPRISE & SOVEREIGN
ACI Enterprise and ACI Sovereign are scoped for on-premise deployment, with locally hosted models and an offline operating configuration.
Keep knowledge, local inference and governance inside your network. Agree access, retention and operational controls with your team.
Locally hosted inference does not incur external model-token or API charges. Hardware, electricity, implementation and support still apply.
Create agents around the workflows you need. Capacity is sized for your workloads, model choices and concurrent use.
Fine-tune specialists on approved examples and evaluate accuracy on unseen business tasks before expanding responsibility.
Offline operation requires local models and internal dependencies. Public model APIs, internet research and external SaaS connectors need connectivity when enabled.
CUSTOMERS & PRIORITY USE CASES
01 / Finance, healthcare administration and legal operations
Detect and mask configured personal data or secrets locally before governed model-based evaluation. Review the post-sanitisation evidence.
What to measure: Detection and masking quality, false positives and data-flow checks.
Explore the workflow02 / Enterprise AI platform teams
Restrict supported tool, MCP, database and shell actions to the operations each workflow is authorised to perform.
What to measure: Blocked forbidden actions, permitted-action success and bypass tests.
Explore the workflow03 / Teams connecting agents to untrusted content
Test governed inputs and actions against deterministic rules and, where configured, a local semantic evaluator.
What to measure: Attack-test outcomes, false blocks and escalation handling.
Explore the workflow04 / Risk, compliance and internal audit
Trace an agent request to its policy verdict and the rule that fired. Export supporting records for the organisation’s own review.
What to measure: Trace completeness, reviewer effort and policy-change history.
Explore the workflow05 / AI operations and service owners
Observe model use, repeated calls and changes in behaviour. Review anomalous patterns and configured limits before extending agent access.
What to measure: Alert quality, unusual-loop detection and response time.
Explore the workflow06 / Finance and engineering operations
Apply configured rules before supported financial actions, destructive queries or shell commands are dispatched. Retain the verdict for investigation.
What to measure: Disallowed-action blocks, approval coverage and exception resolution.
Explore the workflowSovereign governs the agents carrying out these workflows. Enforcement, discovery and evidence coverage depend on the selected integration and configured policies.
Explore more use casesSEE THE WORKFLOW
01
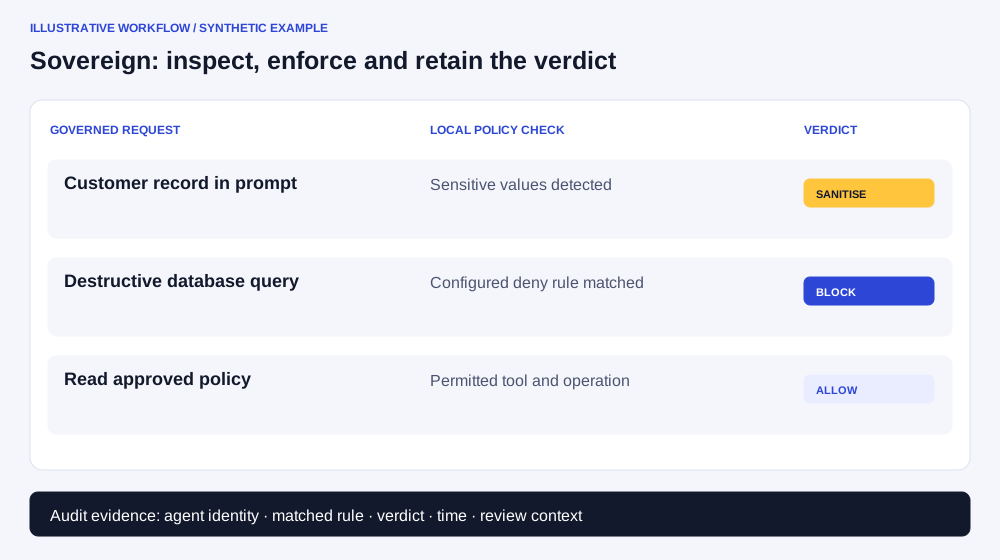
Associate the governed call with its agent and execution context.
02
Run deterministic rules and sensitive-data handling inside the customer environment.
03
Allow, sanitise or block according to the configured rule and supported call path.
04
Record the verdict, matched policy and relevant context for the operator.